Stay informed and regularly check your security procedures to protect yourself, your business, and your customers. Photo via Getty Images

As news comes out every week about new technologies, from new crypto wallets to generative AI to self-driving taxis, it can get overwhelming for most of us to keep up or to understand the new intricacies of technology, and it can get easy to say, “The IT department has it covered.” Well, do they have it covered?

Far too often, companies fail to protect its data with the same muster as its financial security until it is too late. Just as a healthy business will regularly conduct audits of its accounting processes to detect potential fraud, ensure regulatory compliance, and locate areas of improvement for the organization, the same should be done for a business’s data security practices. Key components of any organization are its people and its information, and the IT department is in charge of protecting that information.

We as business people need to ensure that the company’s technology personnel are indeed securing one of the company’s most valuable assets: information.

Big picture: Your business needs to follow an audit process

  1. Confirm the scope of your data
  2. Conduct an internal review of all security practices
  3. Conduct a review of all vendor practices that have access to your data
  4. Confirm compliance with regulations and contractual obligations
  5. Prepare a report with detailed findings and recommendations to improve on year-over-year

Data: What do you have and what duties does it require?

Personal information, particularly when it belongs to customers, is the most frequently compromised type of data. Under laws like the newly passed Texas Data Privacy and Security Act (TDPSA), businesses can have additional obligations to keep this information protected. Personal information can include any information “that is linked or reasonably linkable to an identified or identifiable individual.”

Sensitive data also requires extra precaution, which means protecting (1) personal data that reveals racial or ethnic origin, religious beliefs, mental or physical health diagnosis, sexuality, or citizenship or immigration status; (2) genetic or biometric data that is processed for the purpose of uniquely identifying an individual; (3) personal data collected from a known child; or (4) precise geolocation data.

Other types of data to watch out for include the business’s intellectual property, anonymized customer data, employee personal information, and any other type of proprietary business data. Depending on the industry, the cost of a breach of any of these types of data could be incredibly high, particularly for healthcare and finance.

Ultimately, Texas businesses are required to maintain reasonable procedures to protect personal information, and there may be other laws implicated such as HIPAA, GLBA, CCPA/CPRA, BIPA, GDPR, PIPEDA, and many more, depending on where business is done, the industry implicated, and, in some cases, where customers are located.

"But I think the vendor is responsible."

Check your contracts, and check if the law requires you to have a duty to protect the compromised information, as many do. Involve your IT department in the review of technical compliance whenever you are sharing data with a third party. Further, it is important to make sure that however the Data Processing Addendum says the vendor is processing data is how they are actually processing data. To that point, if you are processing someone else’s data, your business also needs to be doing what it says it is doing, in contracts with third parties and in your Privacy Policy.

Software as a service arrangements, end user license agreements, and other internet and software-based services may require you to hand over data and not give you the opportunity to customize and shift risk. This is why it is important to thoroughly evaluate what technical protections are in place because the risk and duty may still fall on your business regarding the data of your customers and employees. Ask yourself (or your IT professionals) if the vendor actually needs the data they receive to provide services to you.

Key takeaway: Stay informed

Your business needs checks and balances in place with the IT department to ensure you know what they are (or are not) doing and what they are supposed to do. You need policies and procedures, and they need to regularly be tested.

Do you know where your data is stored, both internally and with third parties? Who controls it? How is it being processed, and is anything being shared? Are encryption procedures in place? Firewalls, Intrusion Protection Systems, and End-Point Detection and Response? Do you and your vendors have Incident Response Plans? Stay informed and regularly check your security procedures to protect yourself, your business, and your customers.

------

Courtney Gahm-Oldham is partner at Frost Brown Todd. Lauren Cole is associate at Frost Brown Todd.
Ad Placement 300x100
Ad Placement 300x600

CultureMap Emails are Awesome

MD Anderson receives $10M gift to launch pancreatic cancer program

med funding

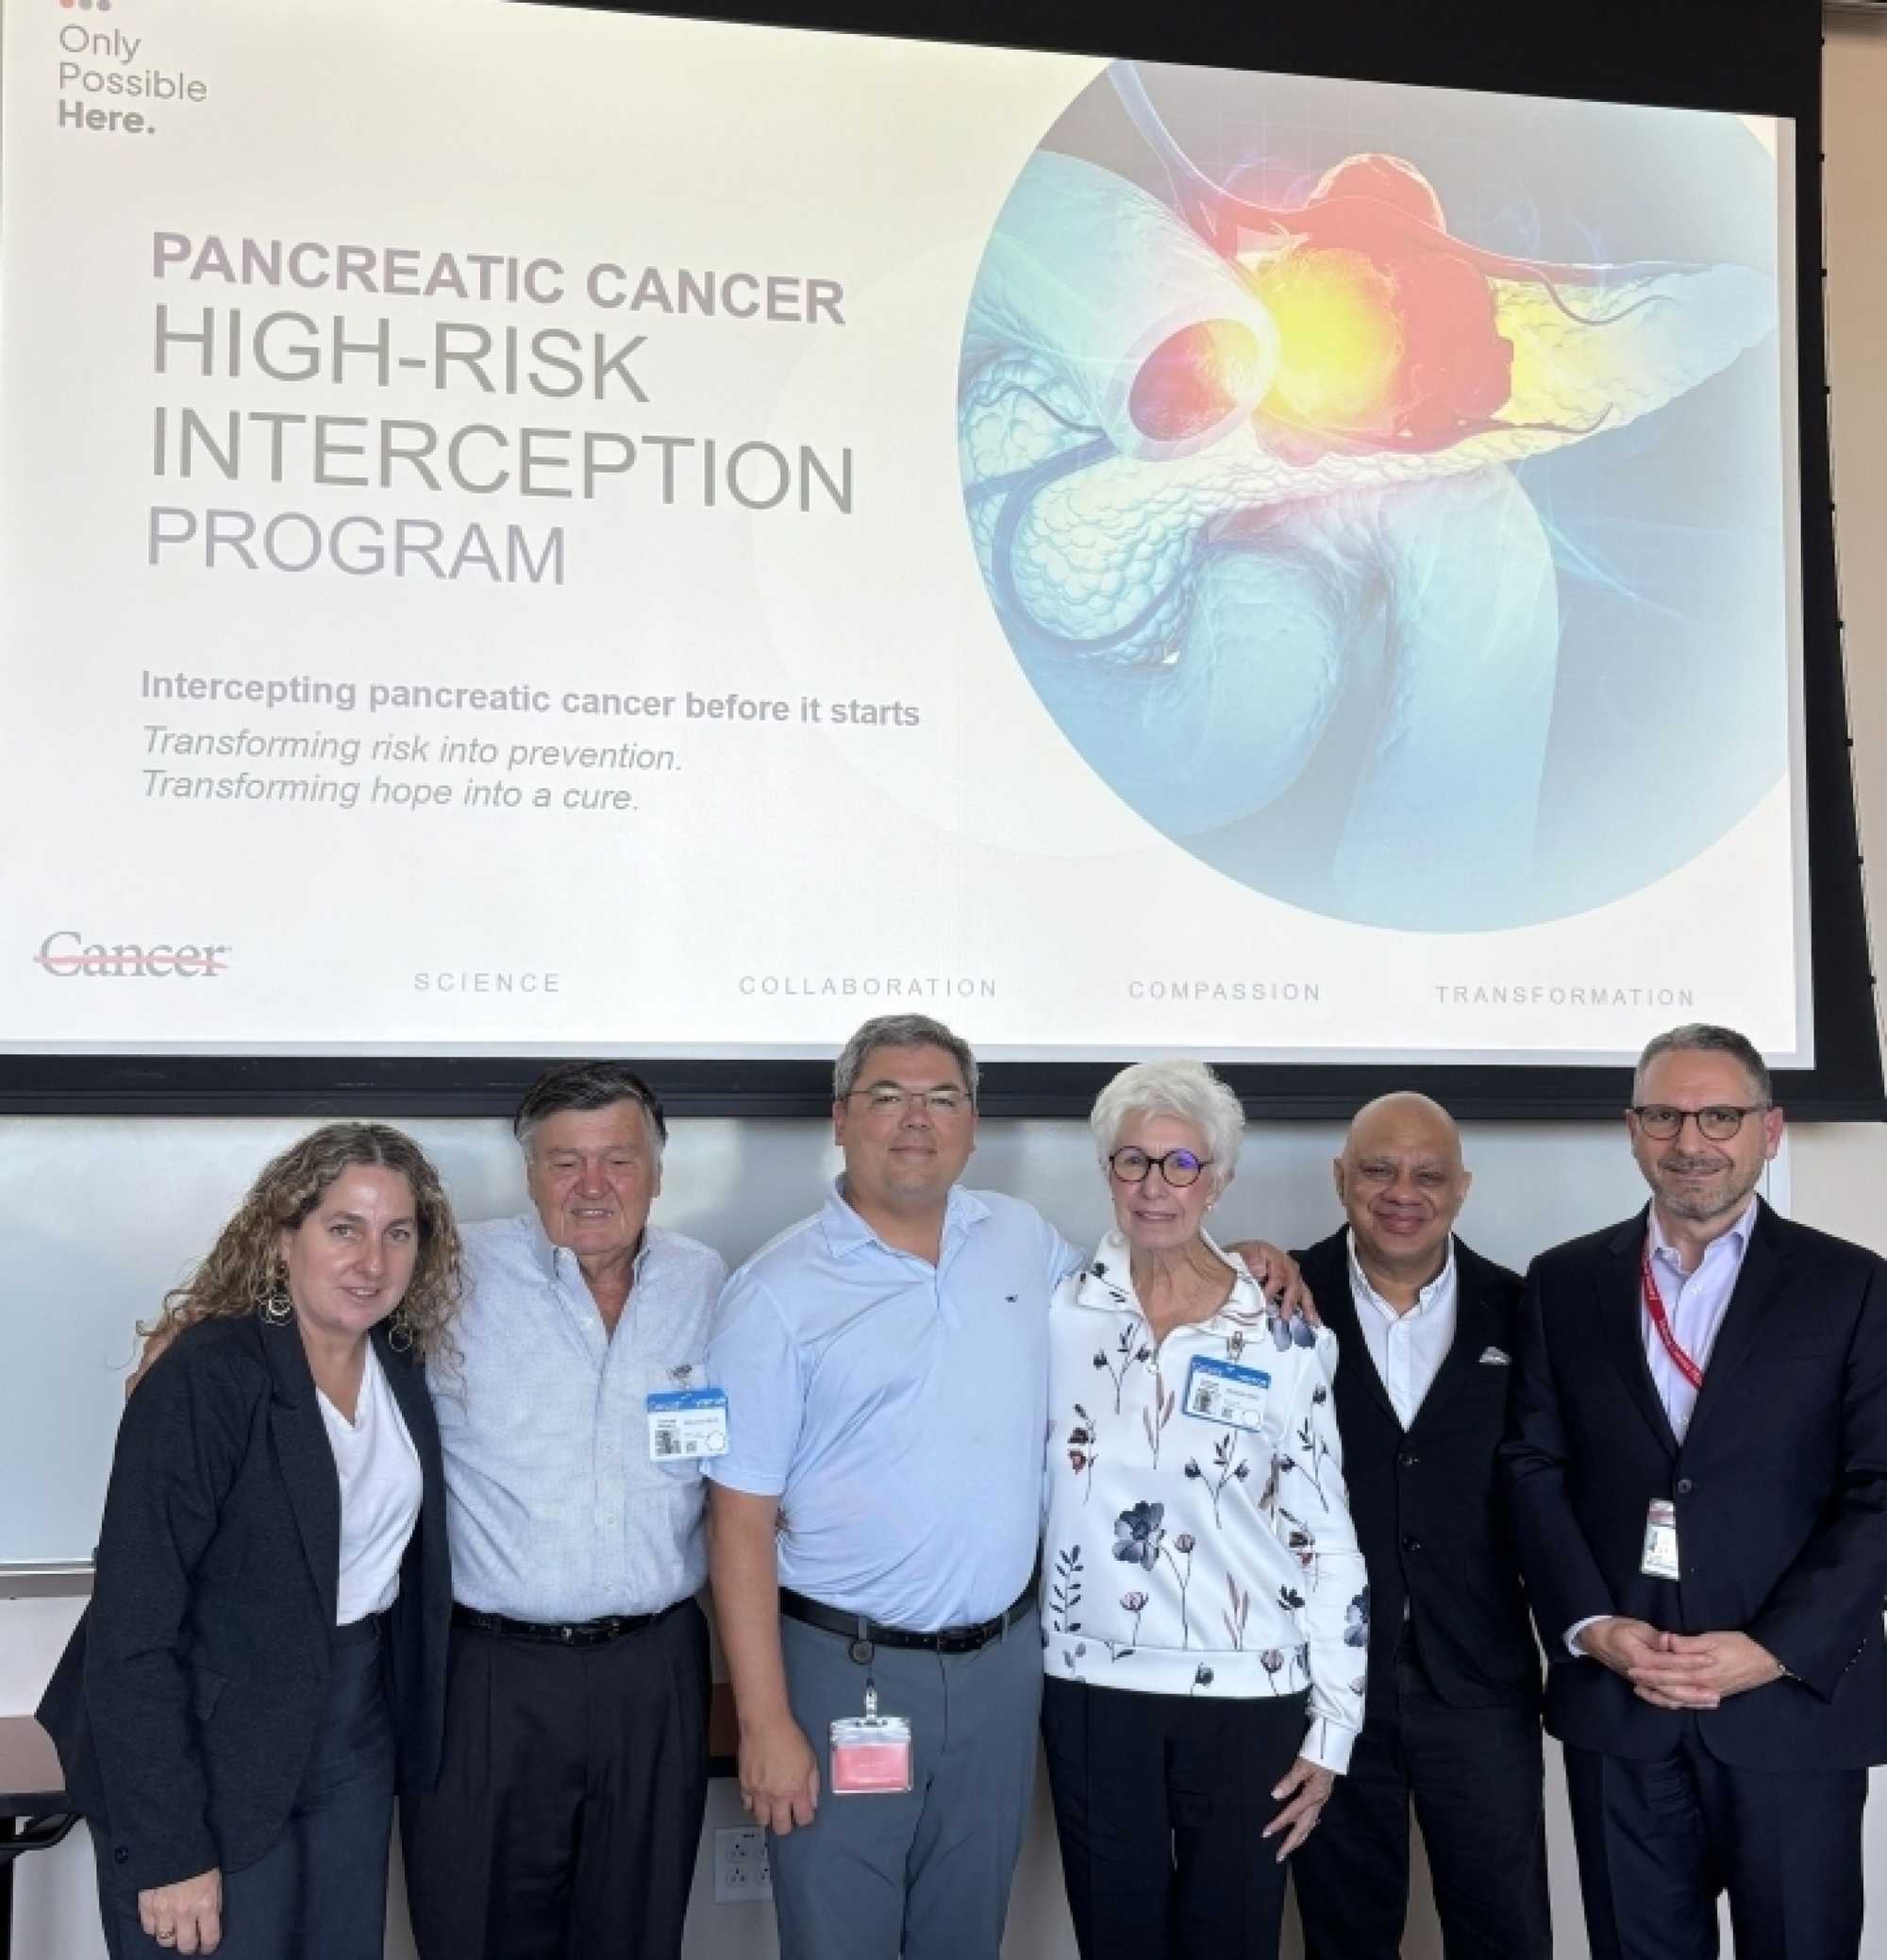
The University of Texas MD Anderson Cancer Center will be getting a significant boost in the fight against pancreatic cancer thanks to a recent gift from longtime supporters Zelma and William Reid. The medical system announced this month that a $10 million donation would help it establish a new Pancreatic Cancer High-Risk Interception Program.

“Philanthropic investments like this create opportunities to accelerate discoveries and pursue bold approaches to some of the most challenging cancers we face,” said Dr. Jeffrey E. Lee, president ad interim of UT MD Anderson, said in a news release. “We are deeply grateful to Zelma and Bill Reid for their generosity and enduring commitment. Their support will help advance innovative research aimed at intercepting pancreatic cancer earlier, when we have the greatest opportunity to improve outcomes for patients.”

Pancreatic cancer is one of the most deadly types of cancer. Despite being relatively rare, it ranks third in total deaths from cancer in the United States. Less than 10 percent of patients diagnosed with pancreatic cancer are still alive five years later.

Dr. Florencia McAllister, William Reid, Dr. Michael P. Kim, Zelma Reid, Dr. Manoop S. Bhutani, and Dr. Matthew H.G. Katz. Photo courtesy MD Anderson

The problem is often detection. The pancreas is located deep in the upper abdomen among many other organs, which can make spotting tumors difficult. Some blood tests can indicate pancreatic cancer, but it is usually not diagnosed until it spreads.

The new Pancreatic Cancer High-Risk Interception Program hopes to assemble new diagnostic techniques and patient screening tools to increase early detection. MD Anderson’s Dr. Michael P. Kim, associate professor of surgical oncology; Dr. Manoop S. Bhutani, professor of gastroenterology and hepatology; and Dr. Florencia McAllister, professor of gastrointestinal medical oncology and genetics, will lead the new program.

The team will rely on advanced imaging, molecular diagnostics, AI-driven assessment, and DNA testing to both create an at-risk patient population profile and hopefully help detect the cancer in its earliest stages. For instance, some of these tools will be able to monitor pancreatic cysts without invasive surgery.

“The ultimate goal is to intercept pancreatic cancer development or to initiate treatment earlier in the disease process, when patients have the best chance for successful outcomes,” Kim added in the release. “This gift will allow us to expand our research efforts, strengthen collaborations across disciplines and accelerate promising strategies to identify and intercept pancreatic cancer before it becomes life-threatening. We are incredibly thankful to the Reids for making this work possible.”

Axiom Space inks partnership to grow semiconductor crystals in orbit

space deal

Down in Webster, Texas, and high above the Earth, Axiom Space and Kansas-based Nitride Global Inc. will grow the next generation of semiconductor crystals in microgravity thanks to a new memorandum of understanding (MOU) signed earlier this month.

“Signing this MOU with Nitride Global reflects the growing commercial interest in producing advanced semiconductor materials in space,” Lucie Low, chief science officer for Axiom Space, said in a news release. “Their leadership in aluminium nitride (AlN) crystal growth and advanced packaging technologies, combined with Axiom Space’s capabilities in orbital infrastructure and mission integration, position us to demonstrate real commercial value in low-Earth orbit (LEO).”

This latest partnership builds on existing collaboration between Axiom and NitrideGlobal and NASA Ames Research Center.

Aluminium nitride crystals are part of the cutting-edge generation of semiconductors essential to emerging high-voltage transistors and also used in various medical technologies. Because of their high thermal stability, they can be used in a variety of environments and applications that have revolutionized everything from electric cars to the grids the cars run on.

However, the crystals are challenging to grow on Earth and face defects and size limitations due to gravity. Growing them in space can enhance their performance, according to NitrideGlobal. Microgravity allows them to grow more uniformly and with fewer defects, potentially resulting in larger, purer and more reliable crystals.

That’s where Axiom Space comes in. The company is developing Axiom Station, a successor to the International Space Station, where new research and manufacturing can be carried out.

“This MOU marks a pivotal milestone in our close partnership with Axiom Space that started as part of the NASA Small Business Innovation Research (SBIR) for AlN growth in space and is now expanding to usher the development of an innovation ecosystem,” Mahyar Khosravi, CEO of Nitride Global Inc., added in the release. “With Axiom Space’s leadership in the in-space manufacturing sector, this partnership will aim to deliver a platform for commercially viable manufacturing of [ultrawide bandgap materials] that will enable the next generation of semiconductor & microelectronics for terrestrial and planetary exploration uses.”

Houston's IAH lands on list of 15 most expensive U.S. airports

Travel Woes

Hold on to those carry-on bags: George Bush Intercontinental Airport is checking in as one of the 15 most expensive airports in the U.S., a new study has revealed.

The analysis from digital commerce and marketing platform ConsumerVoice.org compared the average domestic flight costs at the 50 largest U.S. airports, ranking them from highest to lowest. Flight price data was sourced from the U.S. Department of Transportation’s Bureau of Transportation Statistics (BTS) during the first and second quarters of 2026 and compared with the same period in 2025.

Washington Dulles International Airport in Virginia tops the list as the priciest major airport in the U.S, with domestic flights at IAD costing $534.34 on average. Charlotte Douglas International Airport in North Carolina comes in second place with an average fare cost of $527.79.

IAH lands at No. 13 nationwide, and it's the second most expensive in Texas, the findings show. The typical domestic flight from IAH costs $482.02, and they aren't getting any cheaper. Flights out of IAH are nine percent more expensive than they were a year ago, the report found. The average domestic flight cost $37.80 less in 2025.

Houstonians not only need to be prepared to spend a little extra money when booking their tickets; they'll also need to pack their patience, as IAH also ranks among the worst airports for flight delays and cancellations.

Travelers on a budget can save more on flights out of William P. Hobby Airport, if they're willing to make the drive. Travelers can save about 13 percent on their flights by flying through HOU instead of IAH, but there are other costs to take into consideration.

"Ground transportation, gas, and parking can eat into the difference, so factor these in when choosing the most economical departure airport," the report said.

HOU ranked as the No. 31 most expensive airport on the list with domestic flights coming in at $417.78 on average. Average fares at HOU are also nine percent more expensive than they were last year.

The top 10 priciest major airports in the U.S. are:

  • No. 1 – Washington Dulles International Airport
  • No. 2 – Charlotte Douglas International Airport
  • No. 3 – Detroit metro Wayne County Airport
  • No. 4 – Salt Lake City International
  • No. 5 – Minneapolis-St. Paul International
  • No. 6 – San Francisco International
  • No. 7 – John F. Kennedy International
  • No. 8 – Newark Liberty International
  • No. 9 – Dallas/Fort Worth International
  • No. 10 – Hartsfield-Jackson Atlanta International
---

This article originally appeared on CultureMap.com.